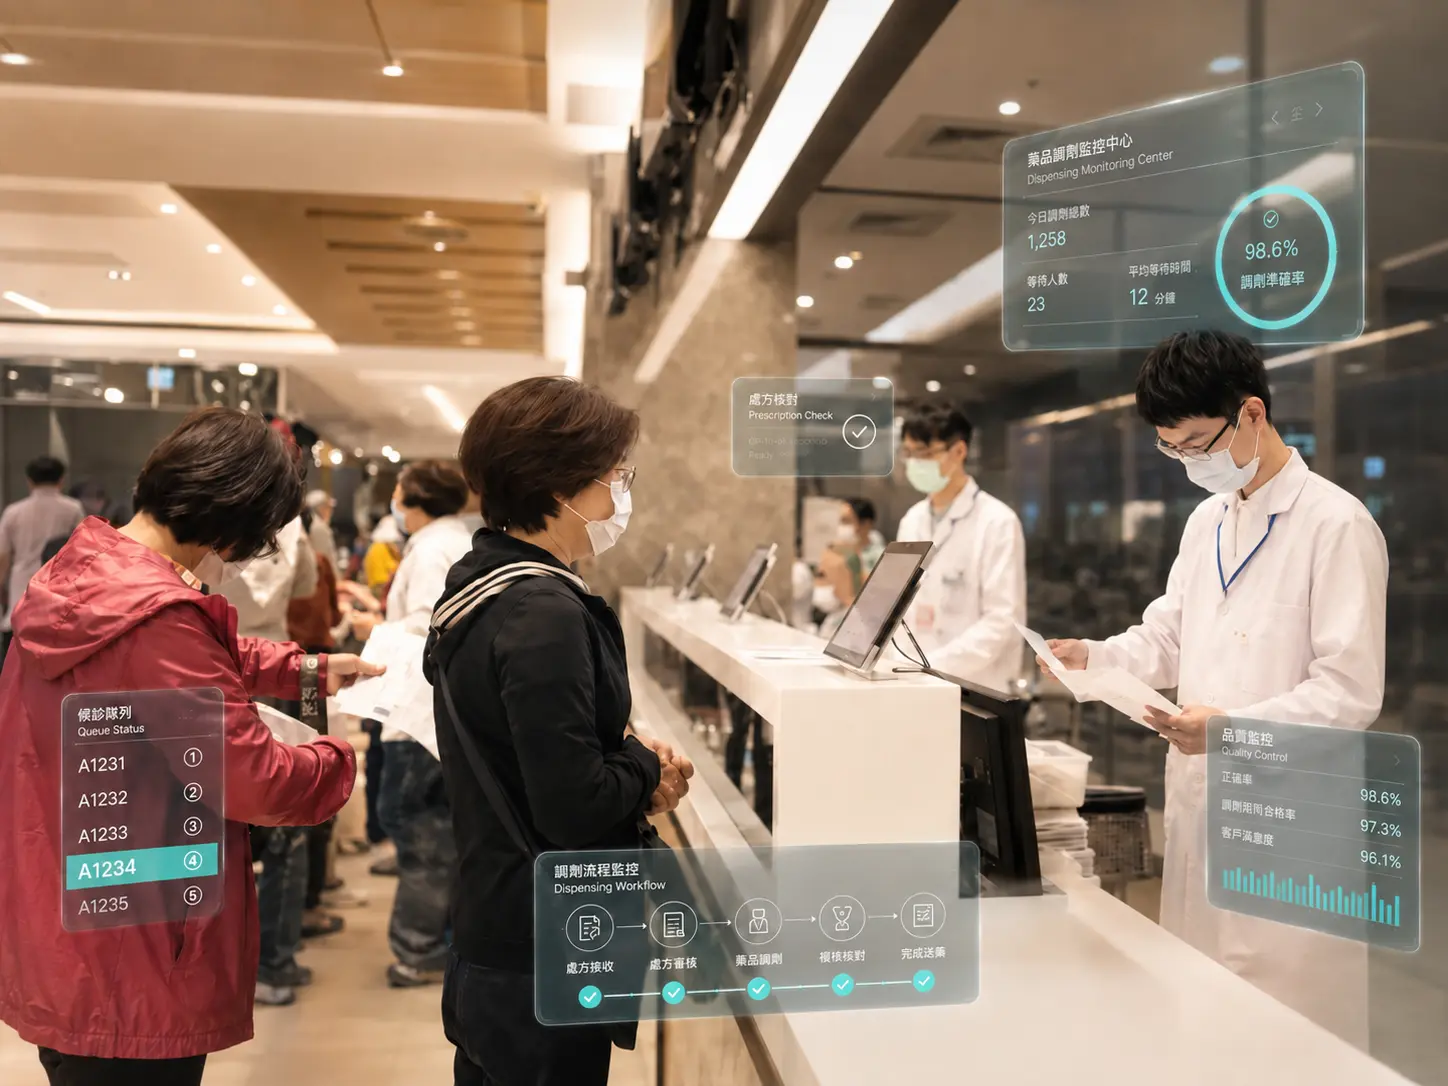
Vitals KPIM provides an industry-first No-Code approach to KPI automation and calculation. It enables quality management teams to independently configure automated KPIs, allowing users to quickly understand indicator status without spending time compiling reports. The system directly retrieves data for computation and presents results through visual report, enabling users to explore data from multiple dimensions and uncover underlying insights simply by operating the platform, significantly improving KPI management efficiency.
System features include:
No-Code Setup and Creation of Automated Indicator Calculation
One-stop KPI management service.
Consolidated Management of Departmental KPI Plans.
Hierarchical Assignment of Indicator Responsibilities.
Visual monitoring reports.
Automated KPI data calculation and anomaly alert tracking process.
Multi-type data analysis module.
TCPI peer KPI comparison mechanism.
One-click generation of submission formats for TCPI.
Galaxy Software Services Corporation
Source Code security management solution 1. Security vulnerability scanning of program code: During the development process, our company will regularly use the program source code scanning software CheckMarx to scan the program code for security vulnerabilities , integrating it into the Secure Software Development Life Cycle (SSDLC)'s CxSuite program code automatic detection mechanism solves the challenges faced by source code security. 2. Data storage security: Our company conducts security control on four parts of data storage: "Capacity Management", "Testing Data Protection Policy", "Backup File Management" and "Password Field Encryption Processing". 3. Preventive measures against computer viruses and malware: All basic information security control, network environment, and server basic information security protection are based on existing information security standards, and various system software and virus codes are updated regularly.
Software control measures
When the operating system is changed, important operating systems or programs should be reviewed and tested to ensure that there are no adverse impacts.
System software or programs should be installed and tested by the system person in charge.
The system person in charge needs to conduct regular inspections, update system security patches, anti-virus software and anti-virus codes to maintain normal system operation.
Development operation control measures: respectively in the requirements and analysis stage, design stage, construction and testing stage, online, subsequent system addition and maintenance, and elimination stage. Each stage has relevant control measures, such as in the design stage:
Taking security needs into consideration, system development should meet security requirements: user identity authentication, system role division and access control, system input and output verification processing, confidential and sensitive data protection, system operation records and storage, such as important systems Logs, use appropriate encryption protection mechanisms, and other security control measures that need to be considered.
During the construction and testing phases, the test environment should be separated from the formal environment, etc.
Risk management procedures related to corporate governance are divided into operational risks, financial risks, and information security risks according to risk classification, and are connected to the risk aspects within the company's overall business plan, Relevant business groups, divisions and departments plan their operating plans and formulate detailed execution actions based on risk matters in the risk aspect. (Note: The company uses the balanced scorecard strategy map model for operational strategies and plans. The balanced scorecard originally covers 4 aspects, and GSS Information added a fifth aspect as the risk aspect.)
The Operations and Quality Management Office of the Operations Management Division is responsible for the analysis and management of risks (and opportunities) faced by the company's quality control system on internal and external environment issues, implementing and strengthening project risk assessment and control mechanisms, and strengthening contract-based Various aspects include risk identification and response, as well as information security risks.
Personal data protection plan: In accordance with the Personal Information Law, our company will regulate the four life cycles of "collection", "processing", "utilization" and "destruction" of personal data.
The company has a personal information work task force: The company has established a "Information Personal Information Work Task Force" to deal with "human resources" and "marketing" respectively. ", "Projects and Product Services", "System Management" and "Procurement Supplier Management" and other aspects have established response teams, and established "Party Rights Incident Handling" "Team", "Audit Team" and "Legal Promotion and Education and Training Team" carry out the overall planning, promotion and continuous operation of personal data protection.
Formulate personal data protection policy (1) Formulate and commit to a personal data protection policy and continue to promote improvement. (2) Comply with the "Personal Data Protection Management Measures": GSS Company shall establish a management system to provide appropriate protection in accordance with the "GSS Personal Data Protection Management Measures" and other procedures and regulations, taking into account the business content and scale of each department Personal data. Furthermore, while collecting, using, and providing personal information correctly, appropriate response measures should be taken to the data subject (the person) regarding matters such as informing and correcting personal information.